Setup around your requirements
We work with your team to define data handling, prepare access and provide the context needed for human approval.
Give an AI Worker the information it needs to safely get work done—with clear access, agreed data handling and a team responsible for keeping the setup current.
Explore AI for your business30-minute consultation. No commitment.
Whether you’re preparing a client handover, reconciling records, or coordinating an order, your Worker needs the right business context.
Bring your IT or security team into the conversation early.
Explore AI for your business30-minute consultation. No commitment.
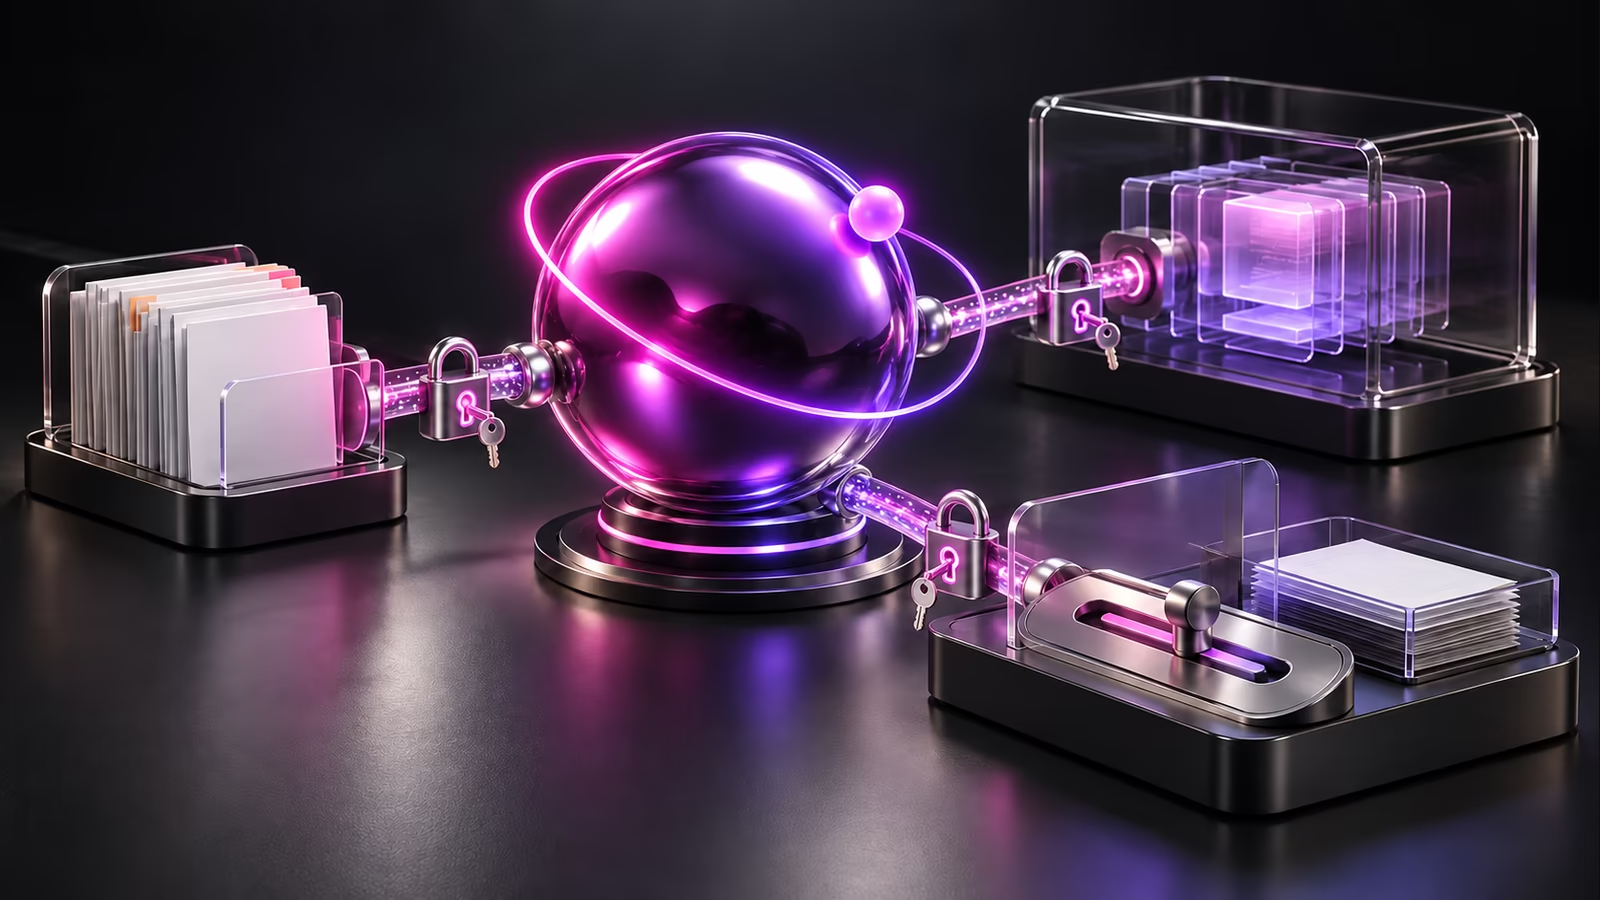
Information flows from your business systems through agreed access to the Worker, then through action rules to the agreed destination. Human approval is required only for the actions you agree. The Worker can also exchange information with a selected AI model and stored information. Authorized support has a separate access path.
The operating environment where the Worker follows your instructions and coordinates the work.
Hosting, location, separation and authorized access.
The operating environment where the Worker follows your instructions and coordinates the work.
Hosting, location, separation and authorized access.
The responsibility you give our worker determines the access it gets. We identify the information the Worker needs to read and the actions it may take, then shape its accounts and permissions around that.
A Worker can have its own credentials. We also define who can administer or support its environment, how access can be revoked and how your information is separated from other customers. The setup includes the people behind the service.
Your Worker needs the right model and clear rules for your information. We agree both around the job.
We match the job to an enterprise cloud service or a compatible local model hosted in a controlled environment.
Agree which information may be used, where it may go and who can access it. These decisions shape the Worker’s setup.
We select and configure model services so your business data is not used to train general-purpose models.
Agree how long working information, memory and provider-held copies stay, and how deletion works. Different copies can have different timelines.
We confirm encryption for the connections that carry information between your systems, the Worker and selected services, as part of your deployment.
We confirm encryption for stored information in the selected environment and services, alongside access permissions and customer separation.
We review the whole data path, including connected software, fallback models, support access and retained copies. A local model is one part of that setup.
Read the guide to sensitive business dataEvery activity is recorded. You choose who reviews those records and how. We agree the detail needed to understand the work, its outcomes and exceptions, while keeping unnecessary sensitive content out of the records.
We also agree retention and deletion for working information, saved context, outputs, logs and backups. These can have different lifecycles. Provider retention and any required records are considered alongside the active Worker environment.
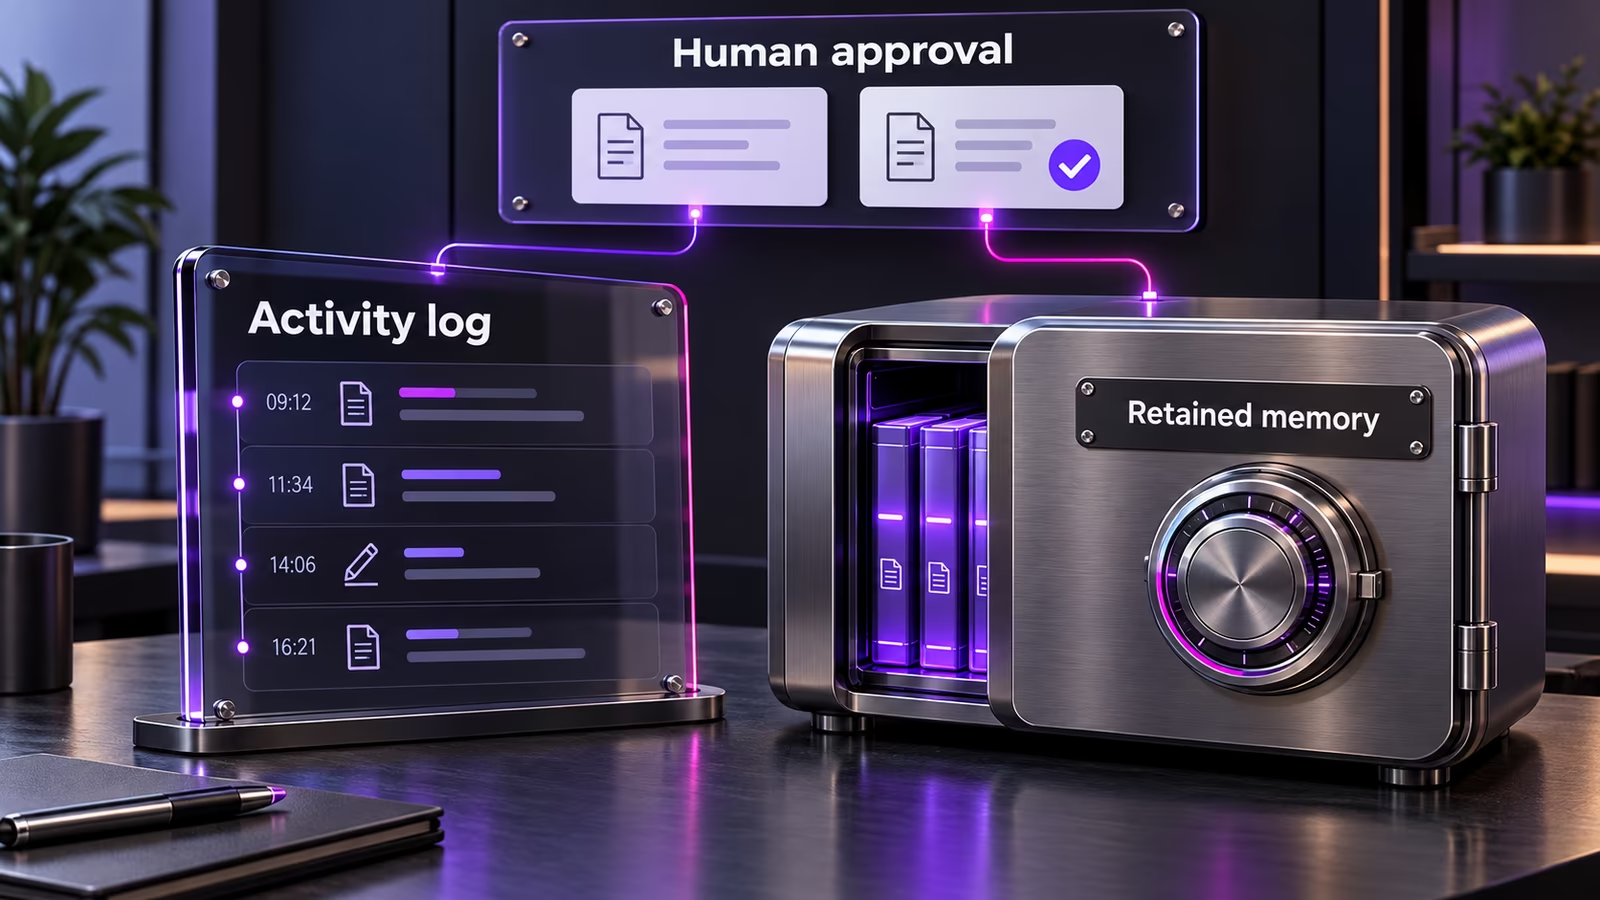
Bring your industry requirements, customer commitments and security policies into the conversation early. We map the relevant requirements to the proposed services, agreements and controls, and identify the evidence needed before sensitive-data processing begins.
An independent examination of a service organization’s controls. The report’s system, scope and date or period matter.
A standard for an information security management system. A certificate applies to its stated organization and scope.
A framework for organizing cybersecurity risk management and controls. NIST does not certify CSF implementations.
For work involving protected health information where HIPAA applies, review the parties’ roles, business associate agreements and safeguards.
Where GDPR applies, review processing roles, purposes, agreements, data rights and international transfers.
Model services are selected and configured so your business data is not used to train general-purpose models.
Agree which actions need approval and when the Worker brings an exception to a person.
Every activity is recorded. You choose who reviews those records and how.
These have different purposes. A provider’s report or certificate is one part of the review; the Worker’s actual configuration and use need to be assessed too.
Read how Workers operatesYou get the Worker and the team behind it. Taurist’s CISO works alongside the people building and maintaining your Worker.
We work with your team to define data handling, prepare access and provide the context needed for human approval.
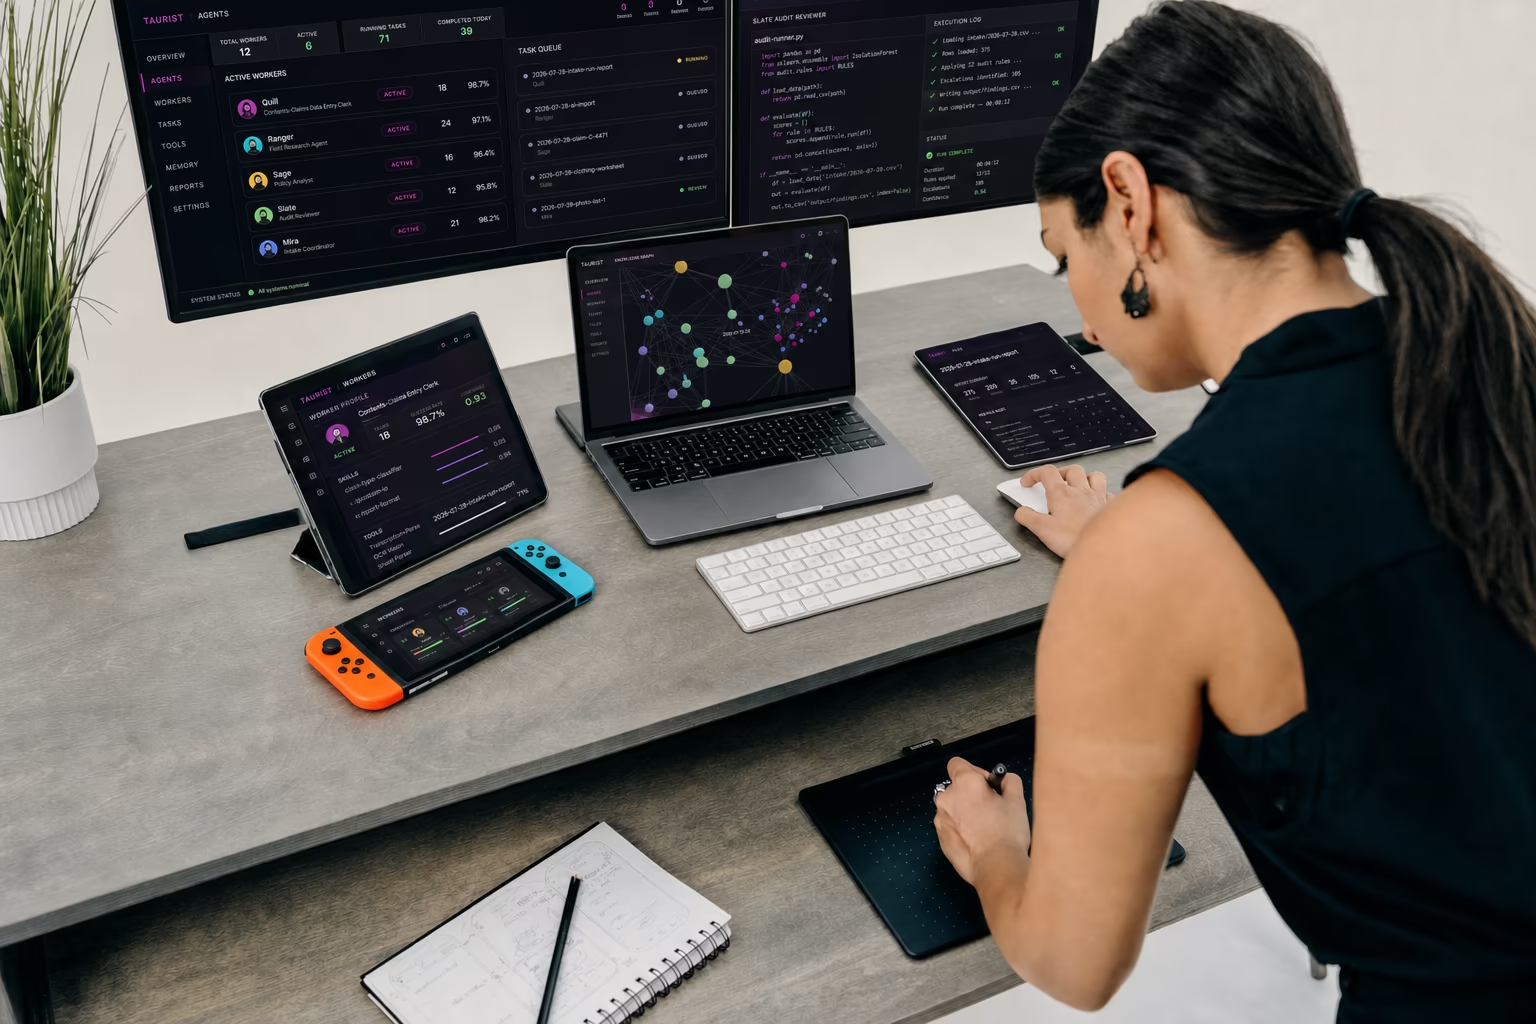
Automated monitoring runs 24/7. We investigate issues, support your team and maintain the Worker and the tech stack it depends on.
Monthly check-ins bring feedback into updates and improvements within the agreed scope. Changes affecting data handling are reviewed against your requirements.
Tell us about the work, your systems and your data concerns. We’ll explore your AI options in a free consultation and send a written summary afterward.
Tell us about the work, your systems and your data concerns. We’ll explore your AI options in a free consultation and send a written summary afterward.
Explore AI for your business30-minute consultation. No commitment.